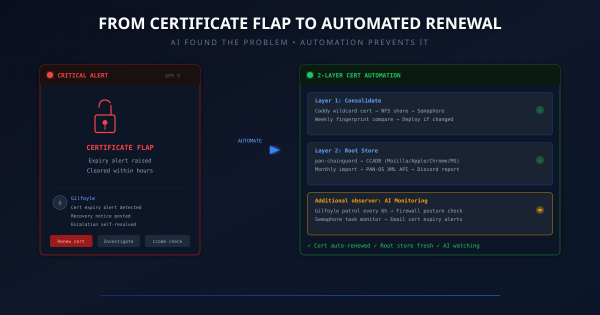
Update, October 14, 2026. This is the April certificate incident and the automation design that followed it. The monitoring schedules below describe that original setup, not a fresh verification of today’s jobs. Gilfoyle now has a Level 4 policy for bounded repairs, but the unattended controller remains inactive. A fresh Discord-route session loaded the new policy; warm sessions retained older prompts. The next chapter explains the rollout. It does not make certificate renewal an AI task.
The Problem # My PAN-OS firewall (GlobalProtect VPN portal at vpn.mareoxlan.com) needs a valid TLS certificate. I had a dedicated LXC (30122) running acme.sh with a Cloudflare DNS-01 challenge to issue a wildcard cert, then a PAN-OS deploy hook to push it to the firewall via the XML API. It worked, but it was a single-purpose VM doing the same job my Caddy reverse proxy already does – Caddy auto-renews *.mareoxlan.com via the same Cloudflare DNS-01 mechanism.
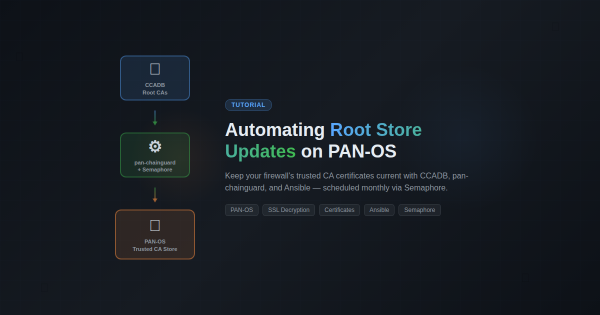
Overview # If you’re running SSL decryption on a Palo Alto firewall, you’ve probably hit this: a user reports they can’t access a website, and it turns out the site’s CA certificate isn’t in your firewall’s trusted root store. PAN-OS only updates its built-in root store on major software releases, which means between upgrades your firewall’s trust anchors slowly go stale.
Enterprise security principles applied to a homelab. This wiki covers the layered security architecture — from next-gen firewall policies to XDR threat detection to certificate lifecycle automation.
Firewall Architecture # The Palo Alto Networks PA-440 provides the network security foundation with App-ID, zone-based policies, and centralized logging. Full details in the Networking wiki — including security zones, VLAN trust levels, and DNS proxy configuration.